
If you're still chasing holiday requests through email, copying sickness notes out of WhatsApp, and checking a shared spreadsheet every time someone asks who's off next Tuesday, you're already doing GDPR employee data management. The problem is that the mess usually feels harmless right up until someone asks for a full record, a manager forwards the wrong file, or nobody can say where a leaver's details live.
For a lot of small UK businesses, the risk isn't a dramatic breach headline. It's the everyday drift of employee records across inboxes, paper folders, laptops, and group chats, with no clear owner, no retention rule, and no reliable way to prove who saw what. That's exactly the environment UK GDPR is meant to control, because employee information such as payroll, performance, and absence records stays within scope of the law, not outside it as “ordinary business information” (GDPR Article 88 and UK employment data guidance).
Table of Contents
- The Spreadsheet Problem Behind Most GDPR Employee Data Headaches
- What Counts as Employee Data Under UK GDPR
- Choosing the Right Lawful Basis for HR and Absence Records
- Building a Practical HR Data Map and Record of Processing Activities
- Setting Retention Rules for Leave, Sickness, and Payroll Records
- Security Controls That Hold Up Under ICO Scrutiny
- Monitoring, Manager Dashboards, and the Proportionality Test
- A One-Afternoon GDPR Employee Data Compliance Checklist
The Spreadsheet Problem Behind Most GDPR Employee Data Headaches
The same story turns up again and again. A receptionist logs holiday in a shared sheet, a line manager keeps sickness updates in a private inbox, payroll stores bank details in a separate file, and somebody else has the rota in a WhatsApp thread. Each piece looks small on its own, but together they create a spread-out employee record that nobody fully controls.
That's the heart of the compliance issue. Employee data sprawl makes it hard to answer basic questions, who has access, what's being kept, and when does it need deleting. The UK GDPR risk is not limited to big central systems, because informal channels still process personal data, and the ICO's employment-record guidance expects employers to think about purpose, need, and retention rather than leaving records scattered across multiple places (ICO employment records guidance).
Practical rule: if you can't quickly list every place an employee record lives, you're not in control of it yet.
The good news is that this is fixable without turning a small business into a legal department. Start by naming the actual storage points, shared drives, inboxes, paper forms, laptops, and messaging apps. Then decide which of those really need to hold employee information and which ones should stop being used for it. That's the practical bridge from chaos to governance.
A useful mindset is to treat the spreadsheet problem as a process problem, not a software problem. A better system only helps if the people around it stop creating shadow records. For a simple benchmark on what manual leave tracking typically costs in time and errors, see this breakdown of paper, Excel, and email leave management.
What Counts as Employee Data Under UK GDPR
Think of a personnel file as a layered folder. The outer layer holds obvious identifiers such as names, addresses, employee numbers, and contact details. Deeper layers contain payroll information, performance notes, rota patterns, disciplinary records, and leave history, all of which are still personal data because they identify a worker directly or indirectly (GDPR employer guide).
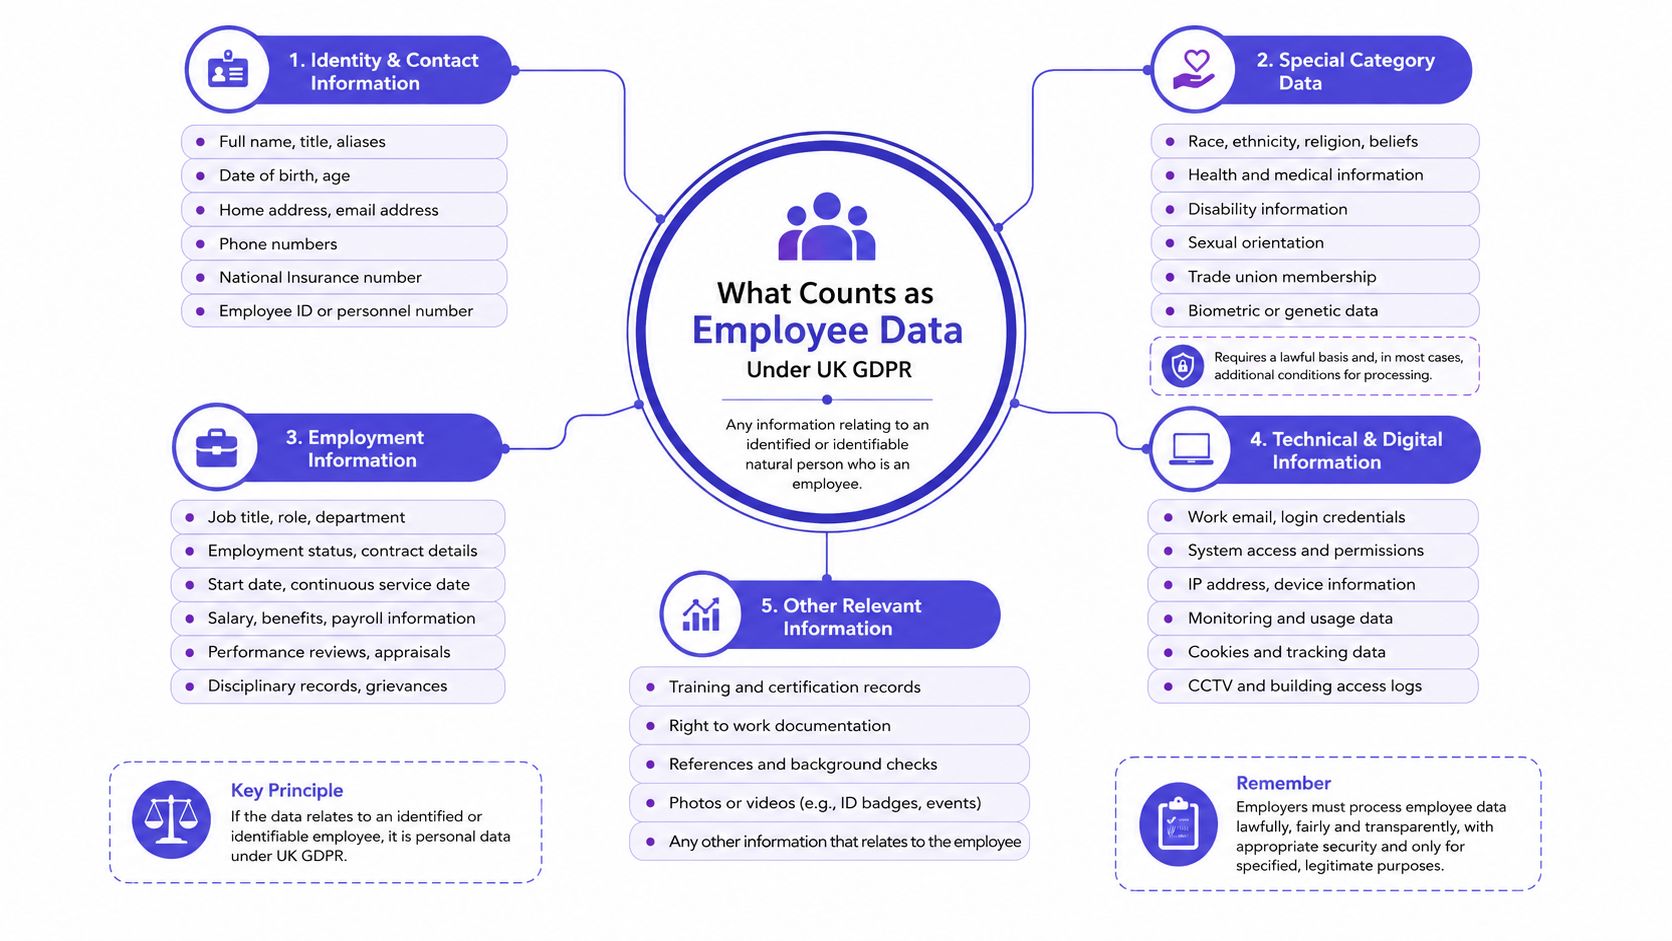
The data many small employers miss
The records that catch teams out are often the indirect ones. Badge logs show when someone arrived. Rota data shows attendance patterns. Absence reasons can reveal health issues. Even a note that looks routine in a manager's inbox may become sensitive if it discusses stress, injury, or treatment. That's why a leave policy shouldn't just list the obvious HR forms, it should cover the quieter records created by scheduling, absence management, and line-manager reporting.
A personnel file should also be read for special-category data, not just regular personal data. Sickness notes, medical certificates, disability information, trade union membership, and biometric clock-in data need extra caution because they can trigger stricter handling requirements. If you're screening volunteers or staff for regulated roles, a volunteer background check can also bring in very sensitive identity and vetting data that must be handled carefully.
Where leave and monitoring data sit
Holiday requests are usually ordinary employee data, but sickness and medical records are not. Remote-work monitoring tools can become more intrusive than managers expect if they capture patterns that go beyond attendance or availability. The same is true of analytics dashboards, which may look harmless until they start exposing health-related absence trends to people who don't need that level of detail.
A sensible classification habit is simple. Ask whether the record identifies the worker, whether it says anything about health or another sensitive characteristic, and who needs to see it. If the answer widens the circle of access, the safeguards need to widen too. That framing makes it much easier to decide what belongs in a general HR record, what belongs in a restricted folder, and what should never be left in a general inbox at all.
Choosing the Right Lawful Basis for HR and Absence Records
A lot of small employers reach for consent because it sounds safest. In employment, it usually isn't. The power imbalance between employer and employee means consent often isn't freely given, which is why HR processing normally relies on performance of a contract, legal obligation, or legitimate interests instead (Cooley employer GDPR guide).
Match the basis to the task
Payroll is the clearest example of performance of a contract. You need bank details, tax data, and working-time information to pay someone properly and deliver the contract they were hired under. Leave systems often sit in this bucket too, because holiday entitlement, contractual benefits, and absence entitlements depend on the employment relationship.
Legal obligation comes into play when the law requires the processing. Right-to-work checks, statutory sick pay handling, and similar compliance tasks belong here because the employer isn't choosing to collect the data for convenience, it's doing so because a legal duty exists. The key is to keep the dataset narrow and document why that information is necessary.
Practical rule: if the data would still be needed even if the employee objected, consent probably isn't the right basis.
Legitimate interests is the basis most often used for operational HR tasks that aren't strictly contractual or legally mandated. Absence trend analysis, workforce planning, and flexible-working reviews often fit here if they're necessary, proportionate, and balanced against the employee's privacy rights. The balancing test matters, especially where manager visibility could reveal more than the task needs.
How to document it without drowning in paperwork
The smartest approach is a short, process-specific justification for each dataset. Payroll identifiers sit in one row, sickness records in another, performance notes in another. That stops businesses from hiding everything under one broad “HR” label and forces a real decision about necessity.
The Ogletree guidance on HR processing makes a similar point, that HR data should be mapped separately in the Record of Processing Activities because the law expects a documented inventory for higher-risk processing and often for larger organisations too (Ogletree on HR data processing risk). For a small employer, that kind of discipline is usually the difference between a defensible process and a messy folder full of unexamined files.
Building a Practical HR Data Map and Record of Processing Activities
A data map doesn't need to be a consulting project. For a small business, it can be a one-day inventory in a spreadsheet with five columns, system, data held, lawful basis, retention, and access rights. That's enough to expose the hidden overlap between HR, payroll, and line-manager records without overcomplicating the task.
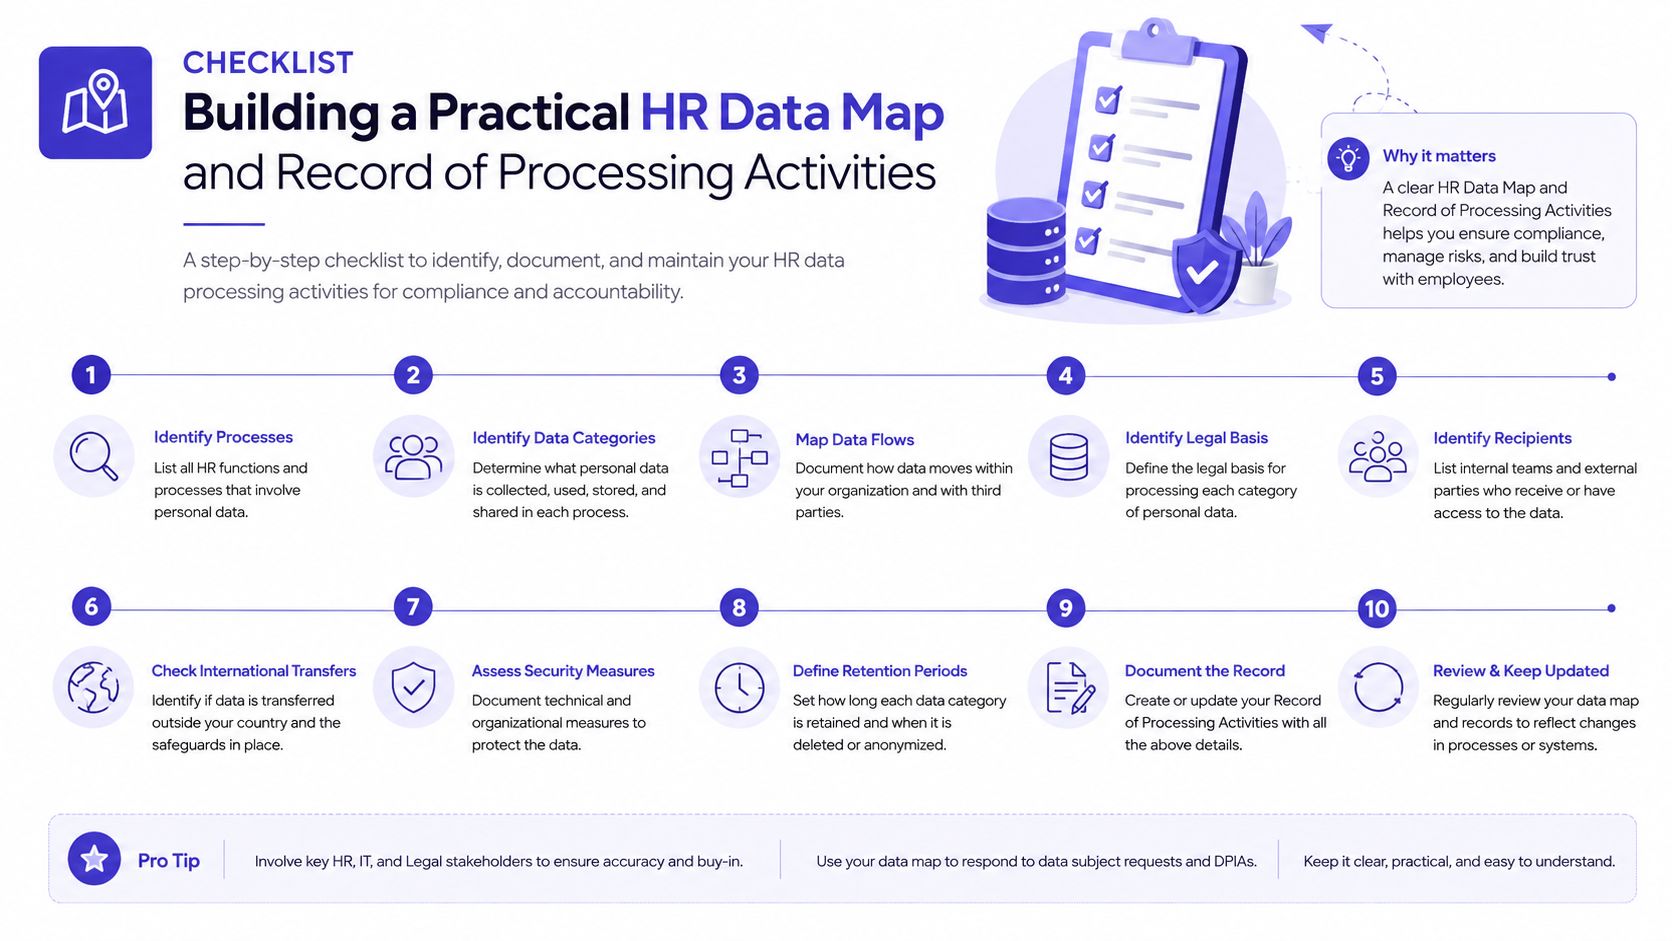
What to put on the inventory
Start with every place employee data is stored. That means spreadsheets, cloud folders, payroll platforms, email inboxes, paper files, shared calendars, rota tools, and any leave system. The earlier section on scattered records matters here because the point is to surface where the data lives, not where the policy says it should live.
Then list the processing purpose for each item. Payroll data exists for payment and tax. Absence records exist for workforce management and, sometimes, legal or contractual purposes. Recruitment notes may sit in a separate process altogether. Once each item has a purpose, the lawful basis and retention rule become much easier to defend.
A simple ROPA approach for a small team
The ICO's retention guidance expects employers to decide based on purpose, legal requirements, and necessity, and that logic maps neatly into a record of processing activities (ICO employment records guidance). Even when a business isn't formally large enough to be forced into a full ROPA, it's still worth keeping one. It gives HR a clear trail for SARs, internal audits, and deletion requests.
Practical rule: if a manager can't explain why a file exists, the record map should probably not show it as active processing.
A 25-person company can usually build this around three live systems. Leave data sits in one tool, pay data sits with a payroll provider, and employee correspondence sits in Gmail or Outlook. The same worker appears in all three, which is exactly why the map matters, it shows which process owns which part of the record and prevents accidental duplication from being treated as a single, permanent personnel archive.
Setting Retention Rules for Leave, Sickness, and Payroll Records
Retention is where small businesses usually go wrong in both directions. Some keep everything forever because deletion feels risky. Others wipe files too early and lose the evidence they need for payroll queries, legal issues, or a subject access request. The ICO's test is practical, keep records for the purpose they were collected for, any legal requirement, and only as long as they're needed (ICO employment records guidance).
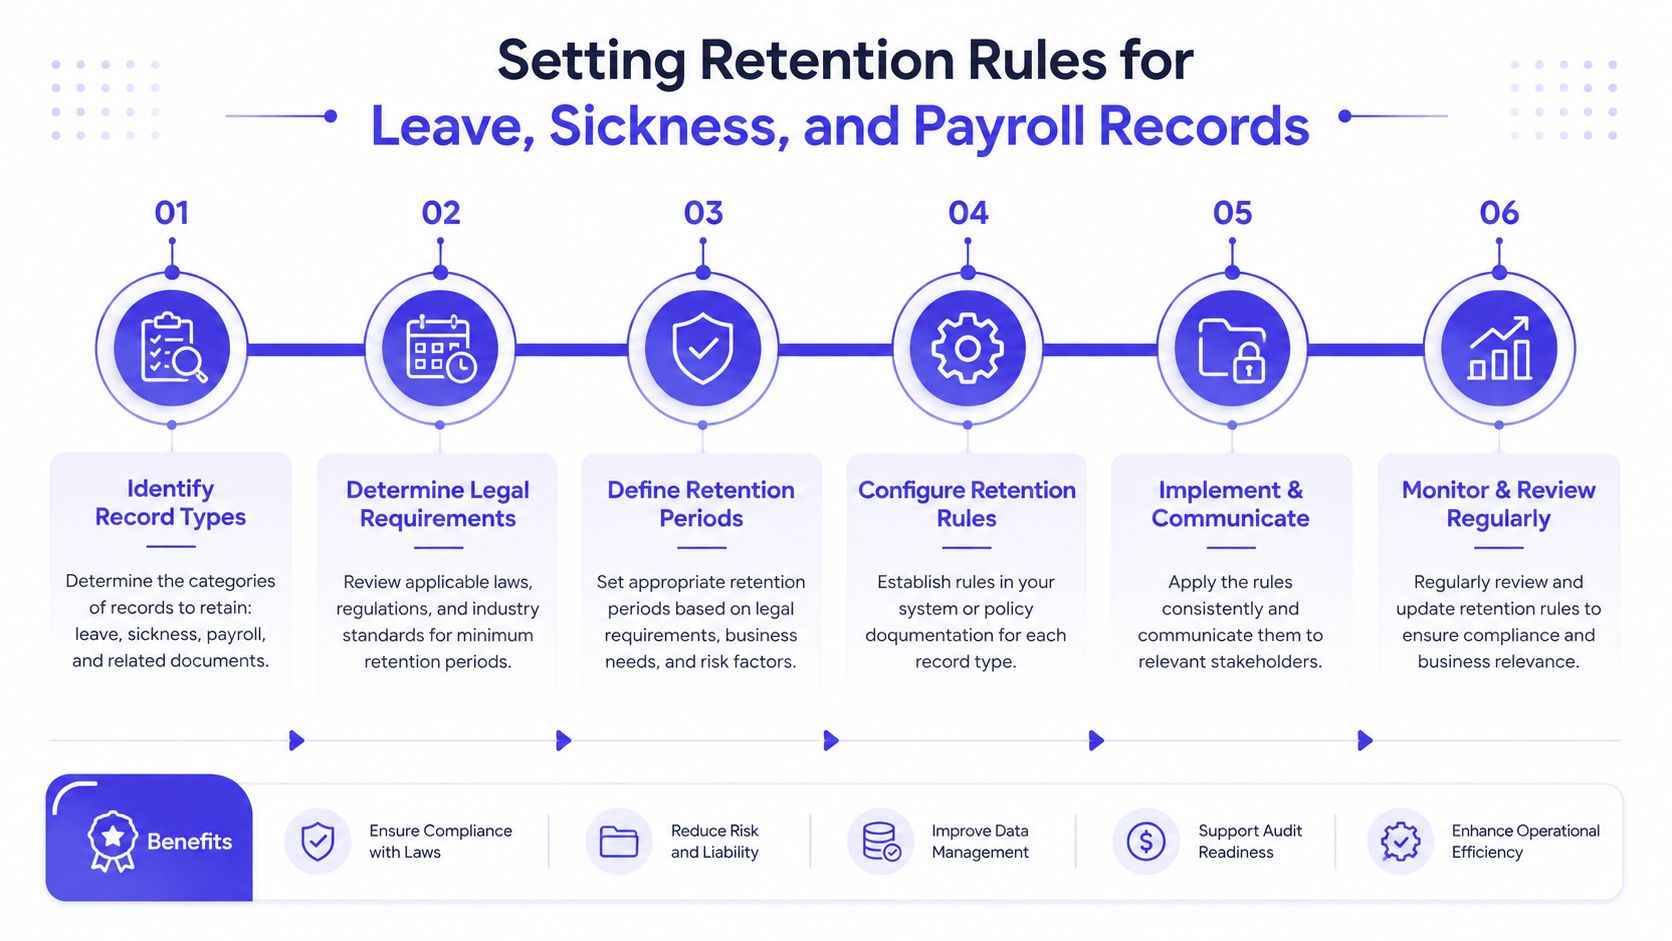
Write the schedule by record type
Holiday records should be kept long enough to answer entitlement and pay questions, then deleted according to your documented purpose. Sickness records need tighter handling because they can contain medical information. Payroll records need to stay available for tax and pay reconciliation, and right-to-work or recruitment records should be treated separately from day-to-day HR files.
The mistake I see most often is one retention period for everything. That approach feels tidy, but it's usually wrong. A leave request, a sickness note, and an accident report do not carry the same legal or operational purpose, so they shouldn't share the same destruction date.
Build deletion into the system, not the memory
A retention schedule only works if the system can enforce it. In a spreadsheet world, people forget. In a leave platform, a configured rule can mark records for deletion or archiving on schedule, which is far easier to defend than relying on one administrator to remember every leaver.
The ICO also makes clear that employees can request a copy of their data, and employers must respond within 30 days to a subject access request (ICO employment records guidance). That makes retention a live operational issue, not a theoretical one, because you need to know what still exists when the clock starts.
For sickness and absence records, a practical reference point is this UK employer guide to sickness absence records. If someone asks to keep a reference beyond your standard retention window, handle it as a separate decision with a clear purpose and end date, not as a casual exception that becomes permanent storage.
Security Controls That Hold Up Under ICO Scrutiny
The minimum acceptable security baseline for HR systems is no longer vague. A UK-focused HR security guide points to encryption at rest and in transit, least-privilege access, MFA, and immutable audit logging as the control set small businesses should expect from any leave or HR platform (Personio HRM compliance and data security). For admin accounts, the expectation is stronger, with mandatory enforcement rather than optional MFA.
What to ask a vendor to show you
Ask how employee data is encrypted when stored and when sent. Ask who can access absence records, and whether managers only see the people they need to schedule. Ask whether the platform keeps logs that show who viewed, changed, exported, or deleted a record, and whether those logs are retained long enough to investigate an incident.
Those answers matter because access control is not just a technical feature. If line managers can see everything, or export it all, the business is effectively making a broad privacy decision every time someone clicks into the system. That's exactly where avoidable exposure happens.
Why backups and logs matter in real life
The same guide recommends daily backups with quarterly recovery tests and audit logs retained for at least 12 months (Personio HRM compliance and data security). Even if your business never suffers a breach, those controls help with accidental deletion, mistaken edits, and the kind of “I thought IT had it” problems that crop up after staff changes.
The internal question to ask is simple. Can the system prove who touched an absence record, restore what was lost, and stop a junior manager from seeing medical notes they don't need? If the answer is vague, the platform may look modern while still behaving like a loose filing cabinet.
For a vendor review that stays grounded in practical safeguards, a secure-design checklist is useful, including the kind of questions LeaveWizard raises in its own GDPR secure-by-design guidance. The point isn't to chase perfect security, it's to make sure the system can support the controls the law expects.
Monitoring, Manager Dashboards, and the Proportionality Test
A dashboard that shows absence trends, attendance patterns, or availability can look like ordinary management software, but it still has to satisfy fairness and proportionality. The IAPP privacy analysis on HR and recruitment stresses that workforce tools should be assessed for proportionality and fairness, especially where monitoring could be intrusive or where line managers are given more visibility than they need (IAPP on HR and privacy).
Ask what the tool reveals about employee data
A simple absence dashboard may be fine if it helps scheduling and workload planning. A tool that combines leave patterns with productivity tracking, location data, or detailed manager surveillance is a different proposition. The amount of data collected has to match the business need.
A lightweight DPIA helps here. Describe the tool, list the data fields it captures, note who sees the output, and ask what could go wrong if the visibility is too broad. If the risk only becomes clear after a complaint, the assessment came too late.
Transparency beats surprise
Staff usually accept being managed. They object when monitoring appears without a clear explanation. If a dashboard helps rota planning, say so. If a feature flags repeated absence, explain who sees it and why. Clear communication reduces the chance that a workforce tool turns into a trust issue later.
The UK employment-data context matters here because Article 88 lets member states shape employee-data rules through national employment law, which is why UK practice can't be reduced to a one-size-fits-all EU checklist (GDPR Article 88 and employment data guidance). A practical privacy rule is to keep the monitoring narrow, document the purpose, and make sure line managers only see the level of detail they need.
A One-Afternoon GDPR Employee Data Compliance Checklist
A small business doesn't need a perfect privacy programme to make real progress. It needs a documented one that stops the worst habits, the inbox files, the duplicate spreadsheets, the forgotten leaver records, and the manager-only trackers nobody can explain. The quickest path is to work through the same sequence every time.
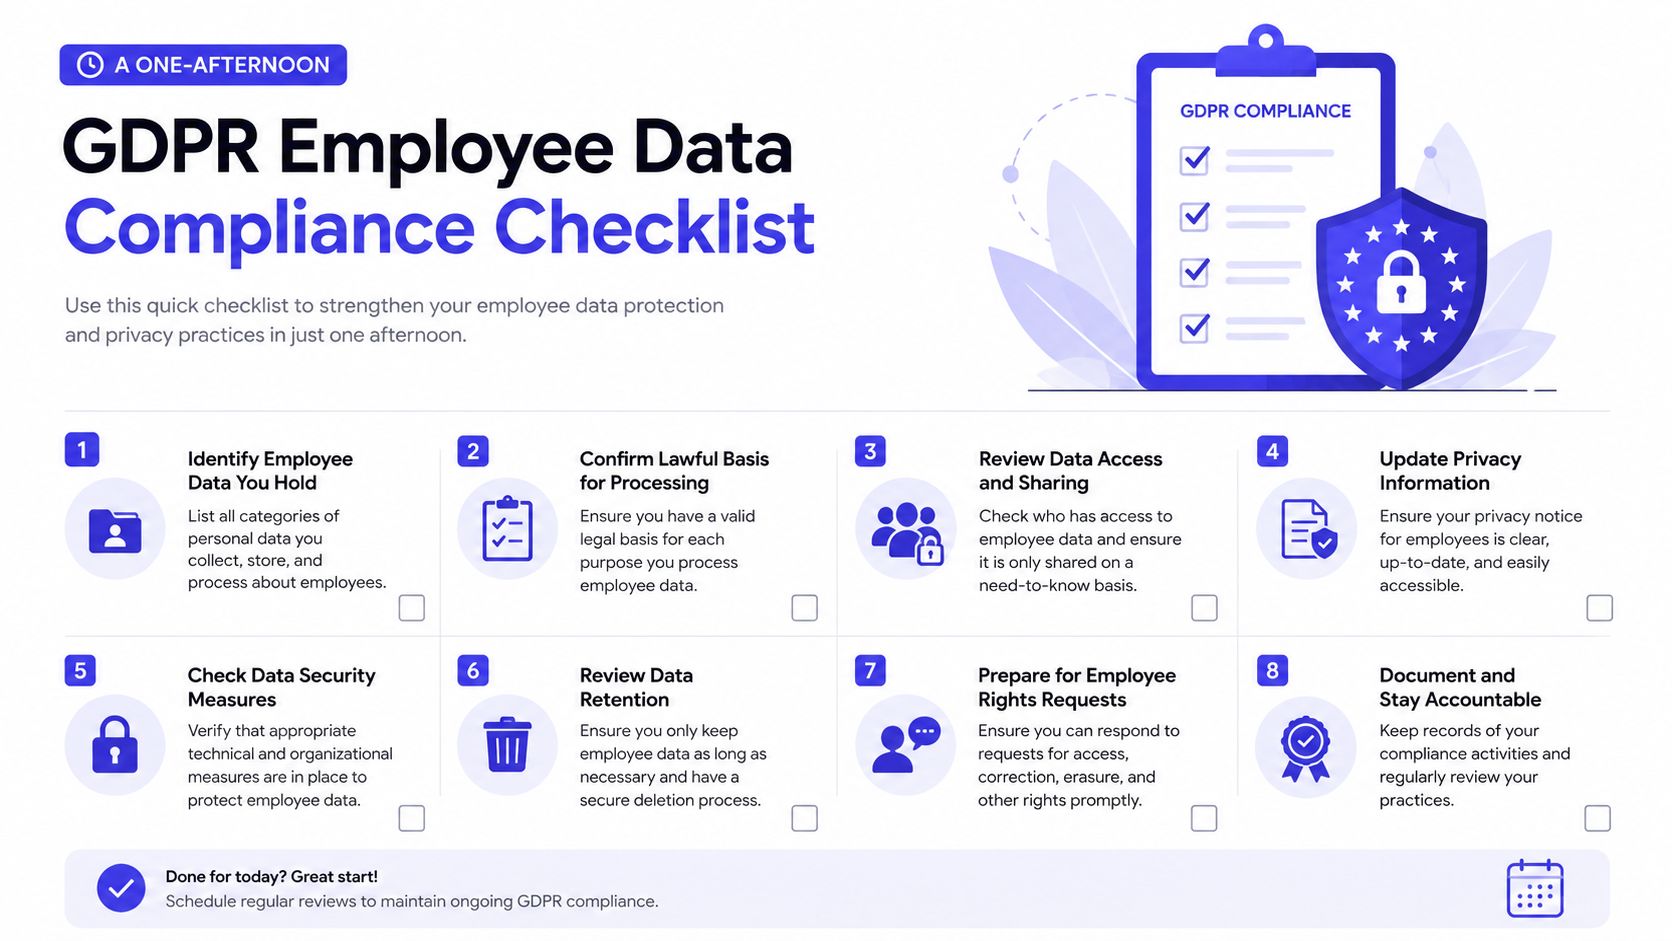
A workable afternoon plan
- Map the records: list every place employee data lives, including spreadsheets, inboxes, shared drives, payroll files, and leave tools.
- Write the lawful basis: assign the right basis to each process, instead of relying on a single HR label.
- Set retention dates: define how long holiday, sickness, payroll, and recruitment records stay live.
- Check access controls: confirm who can view, edit, or export each dataset.
- Review vendor security: ask for encryption, MFA, audit logs, and backup details.
- Prepare the SAR route: make sure there's a clear owner for the 30-day response clock.
- Set breach steps: know who investigates, who escalates, and who decides if a report is needed.
- Remove the clutter: delete or archive stale records that no longer have a purpose.
The ICO's guidance on employment records and the GDPR penalty framework make the same point from different angles, good recordkeeping and reasonable control are not optional when employee data is involved (ICO employment records guidance, GDPR enforcement and penalty scope). If you can't do everything today, do the mapping and retention first. Those two steps usually remove the most risk fastest.


